A White Label Service is a fully customizable offer within the TrustBuilder MFA.
Unlike the standard service (based on Virtual Authenticator and the TrustBuilder Authenticator mobile app), a White Label Service uses different authentication tools:
-
Helium → Browser-based token, fully customizable (UI, colors, logos, templates, etc.).
-
mAccess → Mobile authentication SDK to integrate into your own mobile application
Virtual Authenticator and the TrustBuilder Authenticator mobile app cannot be used with a White Label Service.
Availability
White label service creation is only available to "Enterprise" or "Safe Transactions" clients
Creating a White label service
-
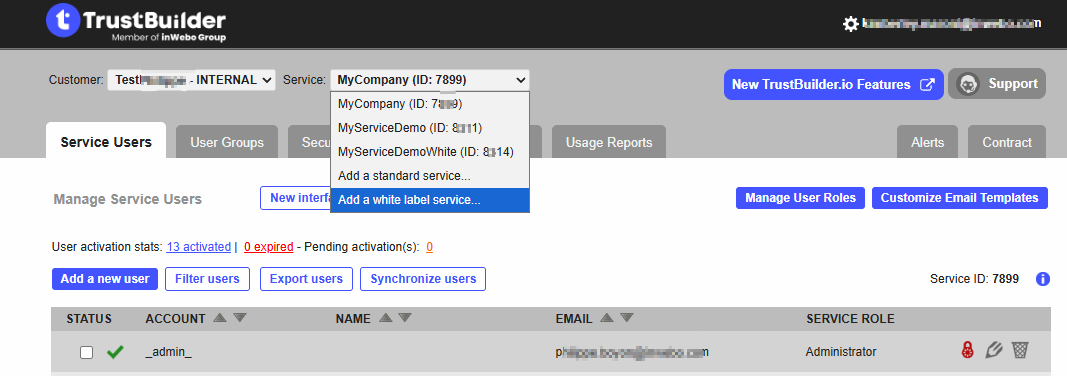
Log in to the Admin Console and select Add a white label service.
-
Enter a service name.
-
Configure the settings (see Settings preferences below).
-
Click Save.
Setting preferences
|
Setting |
Description |
|---|---|
Helium & mAccess
|
|
|
Authentication mode |
|
|
Service password format |
You can select here the format of the password. According to your needs this can be either an alphanumeric password or a PIN code with 4 to 8 digits. |
|
No. retries before locking password |
You can define here the maximum number of tries a user may attempt with his password or PIN code, before locking his access. |
Helium (browser)
|
|
|
Activated |
Users will be able to connect to the "Secure Sites" and applications with Helium. |
|
Template |
|
|
Maximum number of devices |
You can define here the maximum number 'Helium' instances a service user will be able to activate. |
|
Tools automatically blocked after |
You can define here the period of inactivity (in days) after which a Helium device is automatically blocked for users. |
|
Tools automatically deleted after |
You can define here the period of inactivity (in days) after which a Helium deviceis automatically deleted. |
|
Display "push notification" first |
|
|
Display "push notification" only |
|
mAccess (mobile SDK)
|
|
|
mAccess activation |
mAccess activation allows you to add the SDK to your client applications (MFA library for mobile authentication) |
|
Maximum number of mAccess based devices |
You can define here the maximum number of mAccess based applications, a service user will be able to activate. |
|
Authentication with biometrics allowed |
Allows users to use their fingerprint to authenticate with the application instead of their password (It should be implemented by the appropriate mAccess functions in your code/Application) |
|
Authentication with biometrics only |
If you activate this option, your users will be restricted to authenticate with their fingerprint only (This is only possible if the service has been set without password) |
|
Connected OTP |
If activated, authentication requests with connected OTP are accepted. If not activated, they are refused. |
|
Connected OTP format |
You can choose the format based on what your authentication interface supports.
|
|
Connected OTP validity duration (sec.) |
You can define here the duration of validity for online generated (connected) OTPs. In case of complex network infrastructures operating numerous network equipments it might be useful to set this duration to a higher value. This guarantees that the OTP is still valid when submitted to TrustBuilder servers for the final verification. |
|
Offline OTP |
If activated, authentication requests with offine OTP are accepted. If not activated, they are refused. |
|
Offline OTP format |
Choose OTP length and complexity according to the security level required, meaning the probability of finding the correct OTP by luck or brute force: the longer the OTP, the safer it is. |
|
Transaction sealing |
This option allows you to use mAccess to seal transactions with your application. |
|
mAccess timeout |
This is the time in seconds during which your service doesn't request users to type their mAccess password again (for connected OTP only). To generate an offline OTP, users must type their password each time. |
mAccess push notification parameters
|
|
|
No PIN push allowed |
|
|
iPhone parameters |
Settings to configure notifications for applications integrating the mAccess SDK for iOS with APNs.
|
|
Android parameters |
These parameters were used for GCM (Google Cloud Messaging) configuration which is now obsolete. They have been replaced by the Firebase parameters section. |
|
Firebase parameters |
Settings to configure Firebase notifications for applications integrating the mAccess SDK.
|
Custom Authenticator parameters
|
|
|
Firebase parameters |
For a specific version of the Authenticator app that has been modified and has its own notification settings. |
|
APNs parameters |
|
SCIM
|
|
|
Send activation email on creation |
If this option is activated, and if the account has a valid email address, an activation email will be sent when the account is created via SCIM. |
General settings
|
|
|
Push notifications |
|
|
Windows Logon |
Enables or disables Trustbuilder Windows Logon feature - More information |
|
FIDO2 Keys |
Not available |
|
Other settings |
Activate a new device per email If you activate this option, your users will be able activate new devices, by generating new activation codes they will receive on their email address. |
|
Email PIN/password recovery If you activate this option, your users will be able to directly receive recovery codes on their email address to reset their PIN/password. |
|
|
Send an email to users when they activate a device If you activate this option, your users will receive an email each time they activate a new device |
|
|
User login policy
|
|
|
Maximum number of devices of all types You can define here the maximum number of authentication devices of all types a service user will be able to activate. |
|
|
IP Filtering
|
|
Next step
See Helium integration documentation to help you with your integration.